BNM outlines cybersecurity requirements for financial institutions
Annual cyber drills are mandatory under the central bank’s technology risk policy, while threat-sharing arrangements aim to limit risks across the sector.
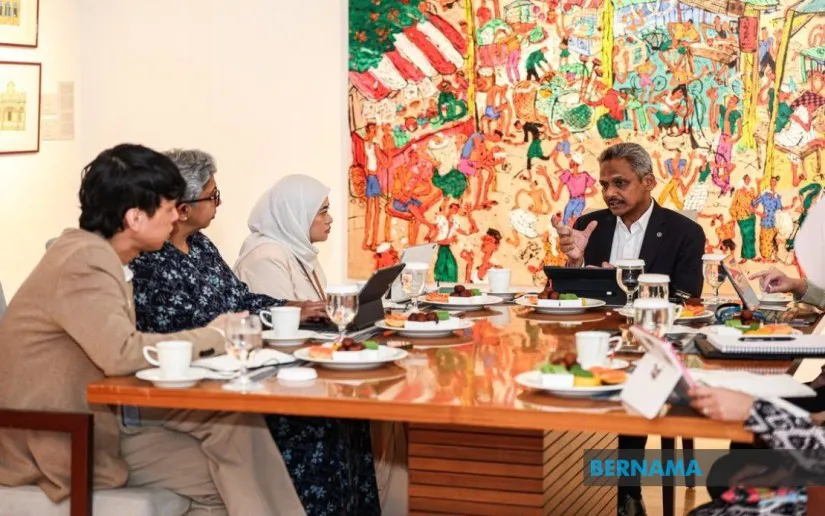
Financial institutions must maintain cybersecurity safeguards under regulatory requirements set by Bank Negara Malaysia (BNM), Governor Datuk Seri Abdul Rasheed Ghaffour said. They are also required to carry out annual cyber drills to assess their ability to withstand disruptions.
Speaking to Bernama, Abdul Rasheed said institutions should take a comprehensive, preventive approach while ensuring they can quickly detect threats and contain incidents. BNM regularly revises its rules and standards to address evolving cyber risks, he added.
The annual exercises, required by the Risk Management in Technology (RMiT) policy document, are designed to uncover system weaknesses and test whether banks can keep operating when their systems are compromised.
Abdul Rasheed said reporting channels and intelligence-sharing platforms allow BNM and financial institutions to exchange information on threats. These arrangements support early detection and help limit the spread of risks between institutions.
Preparedness is necessary regardless of an institution’s size, he said, because interconnected systems mean a weakness at a small bank could put the broader financial system at risk.
During an attack, containment would take priority, including isolating compromised systems and severing connections where needed. Some online operations might need to stop temporarily for investigations and security checks. BNM expects institutions to restore operations with limited disruption while protecting customer data, he said.